-
Regions

Pacific Union
Cultural sovereignty, community identity, and regional digital infrastructure.

Arabian Union
Digital infrastructure, trusted services, and regional modernization.

Americas Union
Cities, states, communities, and private providers building adoption across the Americas.

Africa Union
Mobile-first identity, community growth, and service access.

Europe Union
Digital rights, identity interoperability, and regulated service adoption.

-
Docs
Documentation
The Digital World will provide developers tools to help build the future, including SDKs for various programming languages which go hand-in-hand with documentation and open-source code, and open standards.
FAQs -
Meetings
Meetings
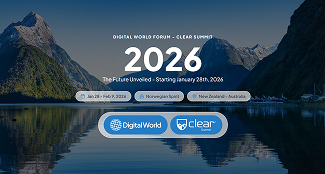
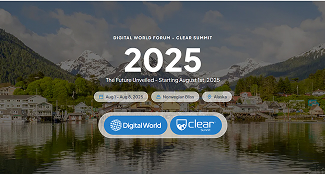
Digital World Meetings will help us connect with like-minded people who share the same value and vision for creating a better future. We're building a new way of living, and we want you to be a part of it.
See all Meetings